Ledger Live Windows 10: What Windows Warnings Mean and Safe Ways to Respond
Safe Ledger Live Windows 10 Install Guide checking belongs before the first launch, not after it: type the maker’s domain by hand, read the certificate, and pull the setup file from that page alone. The tenth edition of Microsoft’s desktop system ships with SmartScreen and Defender, which flag unsigned or freshly published binaries but will not tell you whether a signature truly belongs to the vendor. What follows covers what the companion program does, which machines it serves, how the distribution routes differ, where each one fails, and a five-step verification you can run before the executable touches your disk.
What the desktop companion app is and how it authenticates with your device
The companion application is a desktop interface for a hardware wallet: it displays balances and builds transactions, while the private keys never leave the device. On a tenth-edition machine it runs as an ordinary user-space program, reaches the device over USB or Bluetooth, and demands a physical confirmation on the device before any signature leaves it.
Private keys stay inside the dedicated secure chip
Every signing operation is performed by the hardware device, which holds the seed inside a secure chip the host cannot read. The desktop program sends an unsigned transaction and receives it back signed; it never sees the seed or the derivation path in a form it can export. That split is why a compromised PC cannot drain a wallet on its own – an attacker still needs a physical press on the device’s buttons plus a screen confirmation of the destination address.
What crosses the USB cable
The channel carries public account data and unsigned transaction payloads: extended public keys, addresses, and the firmware images the device verifies before applying. Private material never crosses it in either direction. A malicious host can therefore learn which accounts you hold and can propose a payment, but it cannot sign one, nor alter the amount or destination that the device screen displays during that confirmation.
What the desktop program stores locally
Balances, price history, account labels, and your preferences sit in a local database on the PC, and the program reads them without the device attached. That convenience is also the exposure: a stolen laptop reveals which assets you track and any labels you typed, though not the keys. Encrypting the drive and locking the machine when you step away keeps that metadata out of reach, and clearing local data removes it entirely.
Which devices and accounts does this companion app serve?
It serves owners of the maker’s hardware devices who want to manage holdings from a full keyboard and screen. The desktop build targets 64-bit Microsoft systems from the tenth edition onward, needs a USB port or a Bluetooth adapter, and suits people holding several accounts, using device-adjacent features, or managing more than a phone app handles comfortably.
Hardware floors and supported system builds
Support is tied to the maker’s published compatibility list, which names the oldest system build each release runs on. Older builds lose support as the maker adopts newer runtime libraries, and the tenth edition of Microsoft’s system is now the oldest branch still receiving mainstream security fixes from its own publisher. Read the current list rather than a forum post: the floors move with each release and are published on the official source.
Assets and account types it manages
The program shows each supported coin or token as a separate account with its own address and history. Coverage is not universal: some networks are read-only, some arrive later than others, and newly added assets often require a firmware refresh before the device can sign for them. The maker’s asset page is the authority on which networks are handled natively and which need a separate application running beside it.
When the mobile counterpart fits better
A phone build handles the same accounts and can pair over Bluetooth, which suits one device used at a desk or on the move. It falls short when you need many accounts side by side, when you copy long addresses into a browser, or when you read a full transaction history without endless scrolling. Someone switching between a laptop and a handset can run both and keep the account set in step.
Which distribution route should you pick on a tenth-edition PC?
Take the signed package from the maker’s own domain, verify its digital signature and SHA-256 digest, then run it. That route gives you two independent checks and a recovery path when a check fails. Store listings and package managers add convenience and update plumbing, but they hide the publisher chain you are trying to inspect.
Four routes deliver the same application to a PC. They differ in where the bits originate, whether you can independently verify the publisher, and how much manual work each one costs at every update. The criteria below are the ones that decide whether a route is auditable at all.
| Route | Where the bits originate | Verification you can run | Main limit | |||||||||||||||||||||
|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|---|
|
Research Notice: This article describes generic verification steps. Always consult the vendor’s official documentation for the current release identifier and cryptographic hashes.
Safe Ledger Live Windows 10 Install Guide – this article explains how to obtain the companion application from the vendor’s own repository and confirm its integrity before running it on a 64-bit Microsoft operating system. It covers the difference between official and third-party sources, common acquisition mistakes, and a five-step verification procedure. The Companion Application’s Architecture and Integrity ChecksThe desktop client is a locally running dashboard that communicates with a hardware wallet over USB or Bluetooth, and it validates every firmware update against a cryptographic signature before applying it. This architecture means the official download itself must be verified on the vendor’s official download page, because the client acts as the trusted bridge between your computer and your funds. Code signing and its role in authenticating the packageCode signing attaches a cryptographic certificate to the executable so the operating system can confirm the publisher’s identity. When you launch the downloaded file, the system checks that certificate against its trust store; a valid signature means the binary has not been altered since the vendor signed it. A missing or invalid signature should stop the process immediately, because it indicates either a corrupted file or a tampered package. The certificate’s chain of trust traces back to a root authority, and the vendor’s name appears in the publisher field. The difference between a checksum and a digital signatureA checksum is a short string computed from the file’s bytes, and comparing it against the value published on the vendor’s site detects accidental corruption during transfer. A digital signature goes further: it mathematically binds the file to a private key that only the maker controls, so it proves both integrity and origin. A checksum alone cannot prevent a malicious actor from replacing the file and publishing a matching hash on a lookalike page. Use the signature for security, and treat the checksum as a quick sanity check. What happens if the integrity check failsIf the signature verification fails, the operating system will usually block execution or display a warning about an unknown publisher. You should delete the file and obtain a fresh copy from the maker’s official repository rather than attempting to bypass the warning. Bypassing it increases the risk of running a modified client that could expose your private keys or redirect transactions. A failed check also means the download itself may have been intercepted, so review your network and browser extensions before trying again. Who Needs the Desktop Client and Which Conditions ApplyThe companion application is required for anyone who wants to manage a hardware wallet’s assets, update its firmware, or execute transactions that require the device’s confirmation. It applies to users on a 64-bit Microsoft system with at least the minimum hardware specifications published by the vendor; it does not run on 32-bit architectures or on mobile platforms. Users managing multiple asset accounts and transaction historiesIndividuals who hold more than one cryptocurrency or who need a consolidated view of their holdings benefit most from the desktop client. It aggregates balances, staking rewards, and transaction records across accounts, and it allows batch operations that the hardware device must approve individually. The client also stores historical data locally, which helps with tax reporting and portfolio tracking. For a single asset with infrequent activity, the overhead of maintaining a local application may outweigh the convenience. Hardware prerequisites and operating system version boundariesThe vendor publishes minimum requirements for memory, storage, and processor speed, and these change with each release. A 64-bit edition of the Microsoft operating system is mandatory; 32-bit editions cannot run the current client because the signed binaries target the x64 architecture. You also need an available USB port or Bluetooth adapter for device communication. Because these boundaries shift, check the official source for the latest supported build rather than relying on older walkthroughs. When the web dashboard is sufficient insteadA browser-based interface provided by the same vendor can handle basic balance checks and transaction initiation without a local setup. It works on any device with a modern browser and does not require administrative privileges. However, the web version may lack advanced features such as firmware updates, account renaming, or full history export. If you only need to view balances and send occasional transactions, the web dashboard fits; for everything else, the desktop client remains necessary. Official Repository Versus Alternative Acquisition ChannelsThe maker’s own download page is the only source that guarantees a signed package matching the published release identifier, while third-party repositories, portable builds from forums, and store listings introduce different verification burdens and tampering risks. Comparing them on origin, signature availability, and effort to verify clarifies which channel fits which user. The table below compares five acquisition channels for the desktop client. The criteria are the source of the binary, whether a cryptographic signature is available for independent verification, the typical effort required to confirm integrity, and the user profile for which each channel is suitable. No channel is universally best; the right choice depends on your technical comfort and risk tolerance.
The official vendor site fits most users because it provides a signed package and a published hash in one place. Third-party mirrors suit those behind restrictive networks, but they require extra cross-checking and may lag behind the current release. A portable build from a forum fits only isolated testing where you accept the risk of unverified code. The Microsoft Store listing works for users who want automatic updates and do not mind the store’s review process. Building from source serves developers who need to audit every line before compiling. Why the official vendor site remains the reference channelThe maker controls the signing key and publishes the release identifier alongside the binary, so any deviation is immediately detectable. This channel also receives security patches first, and the vendor’s support team can confirm whether a specific file name matches the current build. When a new version drops, the official page updates its hash and signature at the same time. No other channel offers this single point of truth, which is why independent auditors recommend it as the baseline. Risks of relying on third-party mirrorsA mirror may host an outdated package that lacks recent security fixes, or it may have been compromised to serve a modified binary. Even when the mirror publishes a checksum, that checksum only proves the file arrived intact from the mirror, not that it matches what the vendor signed. You must always compare the mirror’s hash against the vendor’s official value, and if the mirror does not provide a signature, treat the download as untrusted. Time lags also mean you might miss firmware compatibility updates. Common Pitfalls During Download and First LaunchThe most frequent mistake is downloading from a search engine advertisement instead of typing the vendor’s domain directly, which leads to a lookalike page that serves a tampered setup file. Other pitfalls include ignoring the publisher certificate warning, skipping the hash comparison, and running the package without closing other applications that might interfere. Lookalike domains and sponsored search resultsSearch engines often display sponsored links above organic results, and malicious actors buy ads that mimic the maker’s name. These ads lead to domains that differ by a single character or use a different top-level suffix. The page may look identical to the official site and even offer a download button. To avoid this, type the vendor’s address manually or use a bookmark you created earlier. Never click on an ad for a financial application. Skipping the publisher certificate checkWhen the operating system shows a warning about an unknown publisher, many users click through without reading. That warning appears because the binary lacks a valid signature or the signature does not chain to a trusted root. Proceeding runs the package that could have been altered after signing. The correct action is to cancel, delete the file, and re-download from the official source. If the warning persists on a fresh download, the vendor’s certificate may have expired, which the official site would announce. Interference from antivirus or background processesSome security suites flag the client’s network activity or its attempt to access USB devices as suspicious, blocking the deployment midway. This produces a partial configuration that may fail on first launch. Temporarily disabling real-time protection during deployment is a common workaround, but you must re-enable it immediately afterward. Background processes such as other wallet software or browser extensions can also conflict with the client’s device communication, so close them before starting the deployment. How Do You Acquire the Companion Application from the Maker’s Official Repository on a Current Microsoft Platform?To obtain the companion application securely, visit the maker’s official repository, download the signed package for the 64-bit Microsoft platform, and verify its cryptographic signature before running the setup. Have ready a stable internet connection and administrator rights on your computer. Step 1: Navigate to the official download page manuallyOpen your browser and navigate to the maker’s official download page by typing the domain manually. Typing the address avoids sponsored links and lookalike domains that appear in search results. Step 2: Select the 64-bit Microsoft packageLocate the section for the 64-bit Microsoft platform and select the current release package. The vendor labels each build with a version identifier and a publication date, which you will compare later. Step 3: Save the package to a dedicated folderDownload the package file and save it to a folder you can easily find. Keeping the file in a dedicated folder prevents confusion with other downloads and simplifies the verification step. Step 4: Compare the published hashCompute the file’s hash using a built-in tool or a trusted utility and compare it with the value published on the same page. A mismatch means the download was corrupted or tampered with, so you must delete it and start over. Step 5: Check the digital signature in file propertiesRight-click the package, open its properties, and confirm the digital signature shows the maker’s name as the publisher. A valid signature guarantees the binary has not been altered since the vendor signed it. What Changes Between Releases and What Do People Misunderstand About System Requirements?Release identifiers, minimum memory, and supported operating system builds change with each update, and the vendor publishes these details only on its official repository. A common misunderstanding is that a once-compatible computer will remain compatible indefinitely; in practice, newer versions may drop support for older processors or require additional runtime libraries. Version numbering and why old walkthroughs become unreliableThe maker uses a version scheme that increments with each feature release, and the download file name includes that number. Walkthroughs written for an earlier version may reference a different package name, a changed menu layout, or a removed setting. Following outdated instructions can lead you to download a deprecated package or skip a new verification step. Always cross-check the version number on the official page against the one in any third-party article before you act. The myth of permanent hardware compatibilityA computer that ran the client two years ago may fail to launch the current release because the vendor raised the minimum processor instruction set or increased the memory requirement. These changes are not arbitrary; they come from new cryptographic libraries or updated user interface frameworks that demand more resources. The official page lists the current minimums, and it does not guarantee backward compatibility. If your machine falls below the published threshold, you must either upgrade the hardware or use the web dashboard. How to check the current requirements without guessingVisit the official repository and look for a section titled system requirements or release notes. That page states the exact operating system build, memory, and storage needed for the latest version. It also provides the release identifier and the cryptographic hash for verification. Do not rely on forum posts or cached search results, because those may reflect an older release. If the page does not list a requirement you need, contact the vendor’s support channel directly. Q&A:Where can I download Ledger Live for Windows 10 without getting a fake installer?Use only the official Ledger site: ledger.com. Open your browser, type the address yourself, then go to the Ledger Live download page and choose the Windows version. Do not use search ads, sponsored links, Telegram files, YouTube description links, or third-party software sites. After the file downloads, right-click it, open Properties, and check the digital signature. The publisher should match Ledger. If the signature is missing or shows an unknown publisher, delete the file and download again from ledger.com. Also check the file name and size against the page. A fake installer can steal your recovery phrase or change your clipboard. The official installer will not ask for your 24 words. Will Ledger Live ask for my 24-word recovery phrase during Windows 10 setup or an update?No. Ledger Live setup, updates, wallet additions, and firmware updates do not require your recovery phrase in the app. Your recovery phrase stays on the Ledger hardware wallet and is entered only on the device itself when you need to restore it. If any window on your PC asks you to type those words, treat it as a scam. Close the window, disconnect the device, and run a malware scan. The only correct place for recovery words is the hardware wallet screen, not Ledger Live, not a browser, not a support chat, and not a text file. Windows Defender or SmartScreen blocks or warns about the Ledger Live installer. What should I do?First, confirm you downloaded from ledger.com. If SmartScreen says ‘Windows protected your PC’, click More info only after you have verified the file signature and source. You can then choose Run anyway. If Defender flags the file as a threat, do not ignore it without checking. Compare the SHA-256 hash from the Ledger download page with the file hash on your PC using PowerShell: Get-FileHash .\ledger-live-desktop-*.exe -Algorithm SHA256. If the hash matches, the warning may be a false positive; if it does not match, delete the file. For ongoing use, keep Windows 10 updated, keep Defender enabled, and avoid cracks, keygens, and patched installers. Do I need an administrator account to install Ledger Live on Windows 10, and can I use a standard user account?You can download the installer with a standard account, but Windows 10 usually asks for admin approval during installation because the app writes files to Program Files and creates shortcuts. If you are on a shared PC, get the admin password from the owner or install it under your own admin account, then switch back. After installation, Ledger Live can run from a standard account. For better separation, create a dedicated Windows user for crypto activity, keep that account free of unknown apps, and connect the Ledger device only when you use it. Do not let anyone remote into that session while the device is connected. I already installed Ledger Live from a link I am not sure about. How can I check it and clean my PC if it is fake?Disconnect your Ledger device and do not enter your recovery phrase anywhere. Open Windows Security and run a full scan. Then go to Settings > Apps > Apps and features, find Ledger Live, and check its install date and publisher. Compare the installed version with the current version on ledger.com. If the publisher is unknown, uninstall it. Also check Task Manager > Startup for strange entries and review browser extensions. If you typed your recovery phrase into anything, move your funds to a new wallet with a new recovery phrase generated by your Ledger device. After cleaning, download Ledger Live again from ledger.com and verify the signature before installing.
Ledger Live Not Working on iPhone: Fixing a crash or blank screen without risking fundsLedger Live Not Working on iPhone: Force Close and Reinstall Ledger Live Not Working on iPhone: Fixing a crash or blank screen without risking funds 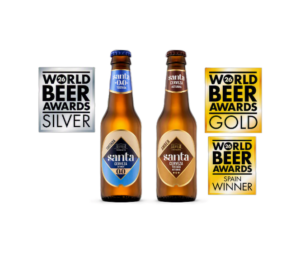 SANTA Amber, mejor cerveza española de su categoría en los World Beer AwardsLa cerveza asturiana de FUENSANTA ha sido reconocida como Spain Country Winner y Medalla de Oro en los World Beer Awards 2026, mientras que SANTA Tostada 0,0 ha obtenido la Medalla de Plata, reforzando la proyección internacional de la marca. Ledger Live: How It Secures Your Crypto Assets Every DayLedger Live: Daily Habits That Protect Your Crypto Ledger Live: How It Secures Your Crypto Assets Every Day These Ledger Live wallet setup and security 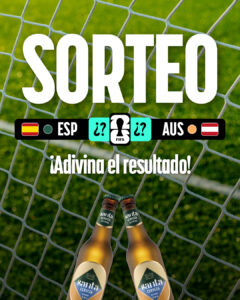 🎁 SORTEO 🎁 FUENSANTA con LA SELECCIÓNPronostica el resultado exacto del España vs Austria en el Mundial 2026, participa en nuestro Instagram y entra en el sorteo de packs de SANTAS. Comenta antes de las 20:55 h y brinda por la victoria.  |